AttackDefense.com [SXSS] - YetiForce CRM
Mission
In this exercise, the attacker already has admin access, so there is nothing more to be done. However, it looks like that admin access does lead to an XSS attack. So you can try to find this XSS as a purely academic exercise.
A version of YetiForce CRM is vulnerable to a stored cross site scripting attack. The following username and password may be used to explore the application and/or find a vulnerability which might require authenticated access:
- Username: admin
- Password: Password1
Objective: Your task is to find and exploit this vulnerability.
Level difficulty: Easy
Category: Real World Webapps > Stored XSS
Solution
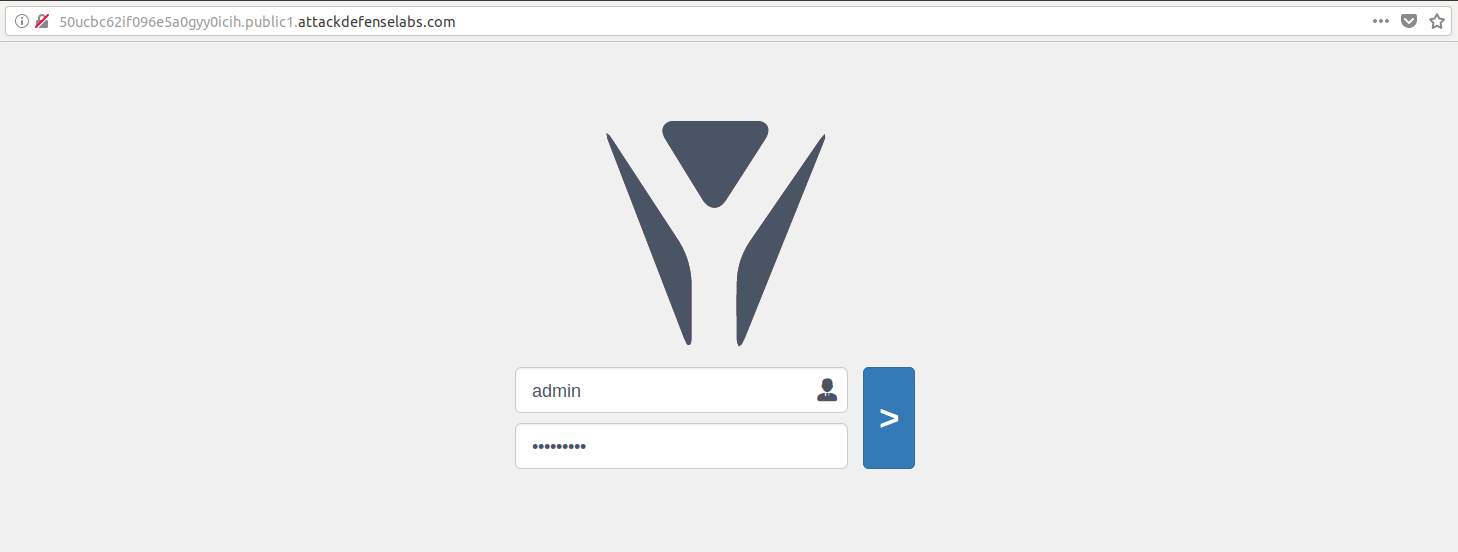
At first, I was taken straight to the application login, and by using the username and password provided above I was able to gain access to the application backend.
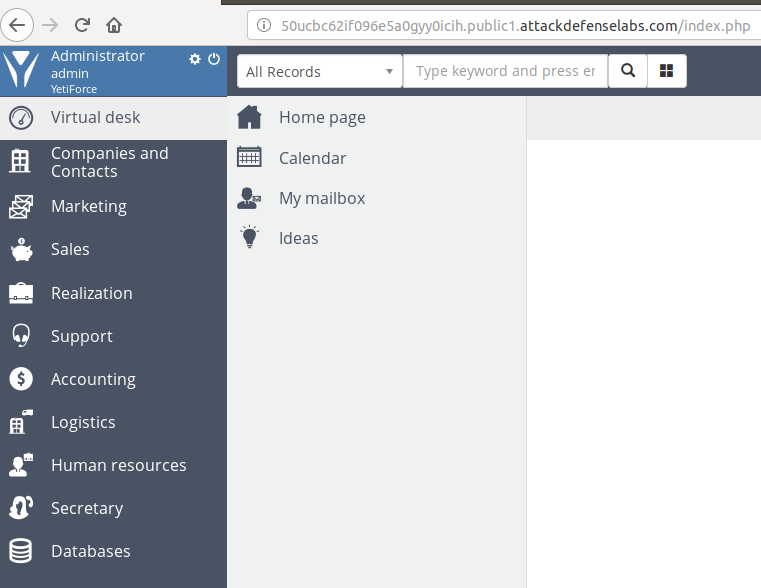
Straight after logging in, we can see that the footer section of the application lists the version as 3.0.0.

Not knowing where to start, I decided to use @GetSploitBot for Telegram in order to obtain exploits based on the provided information: “A version of YetiForce CRM is vulnerable to a stored cross site scripting attack.”
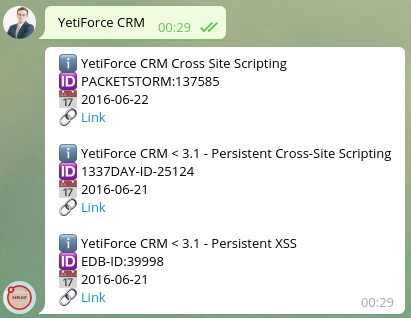
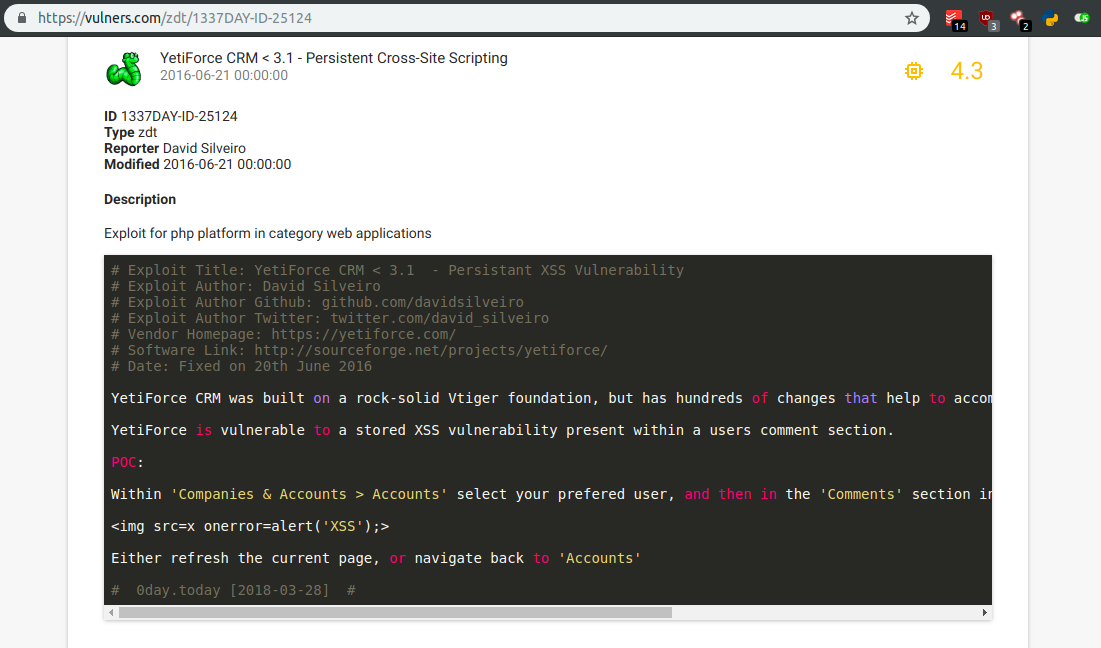
By accessing the following link, we can observe the path and the input field described in the exploit.
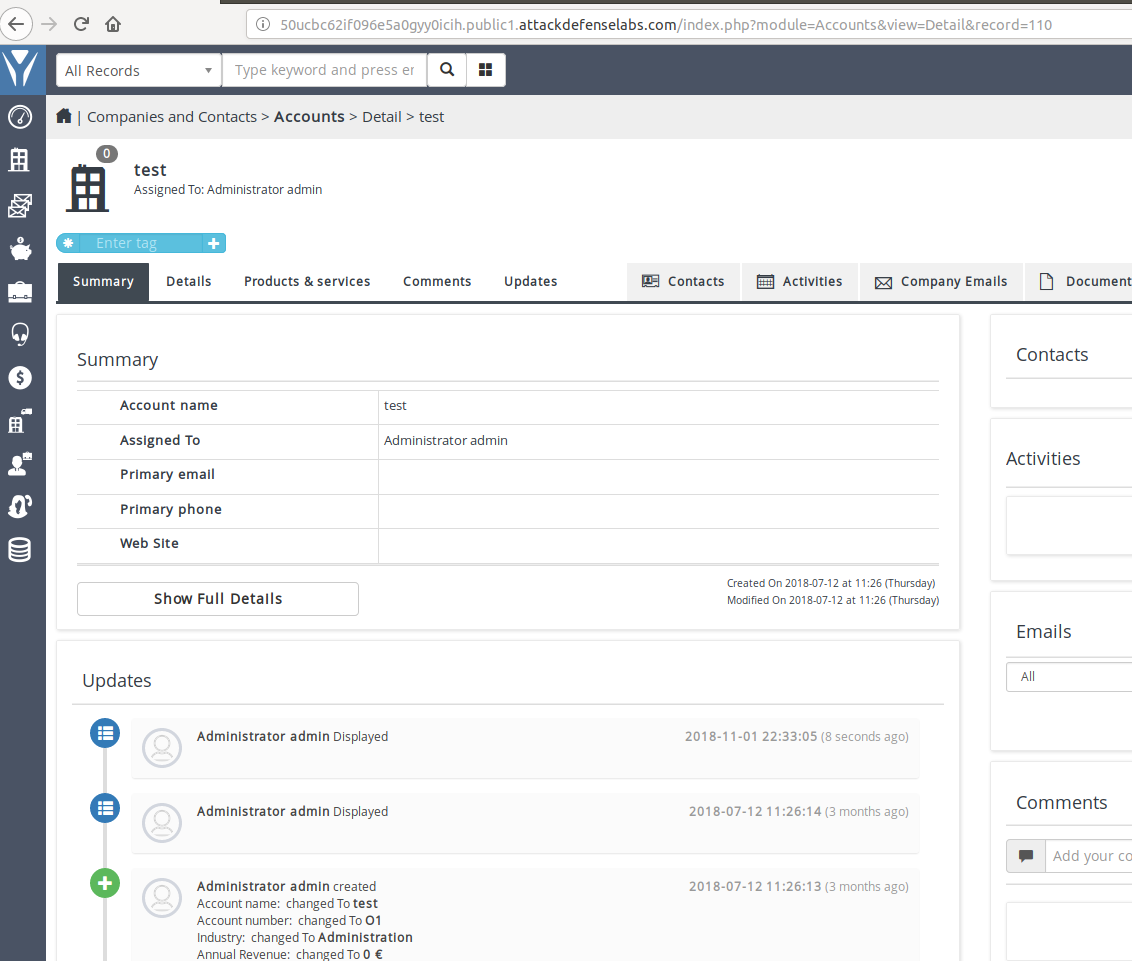
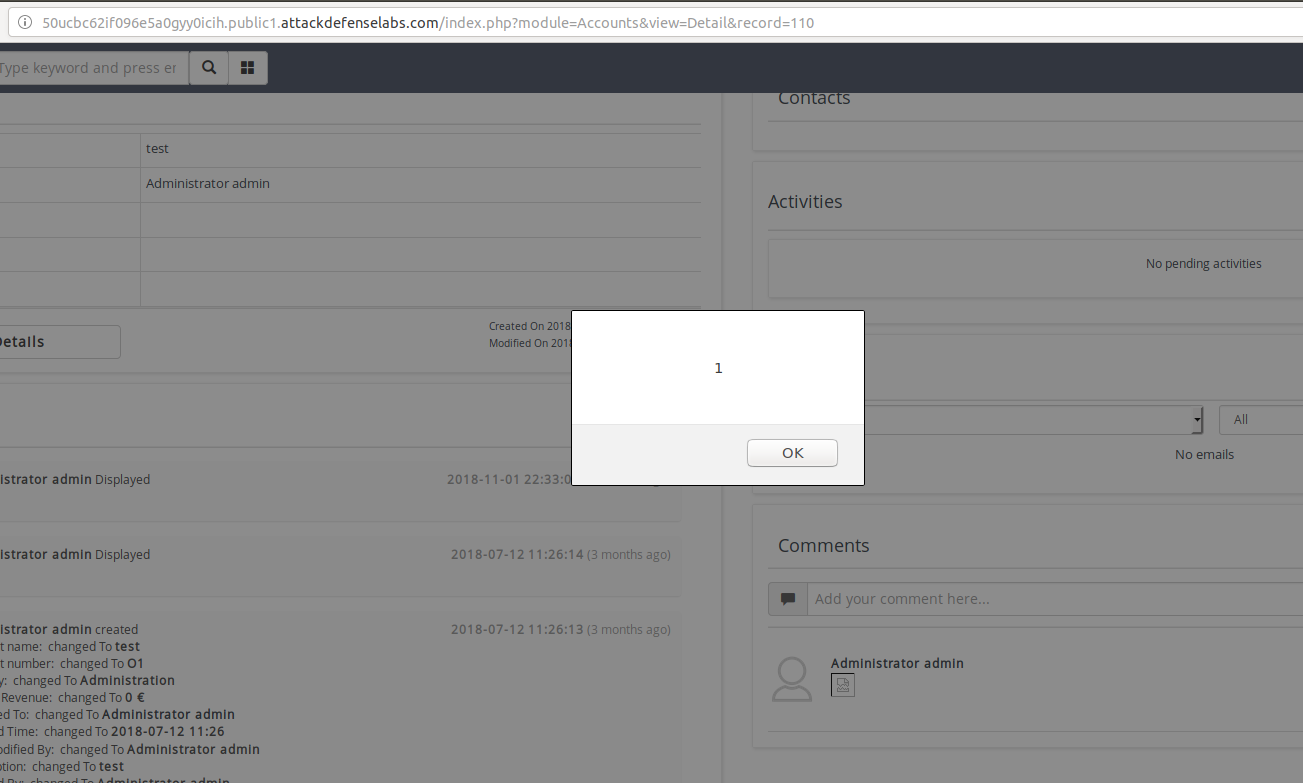
I set my payload as follows in the comments input:
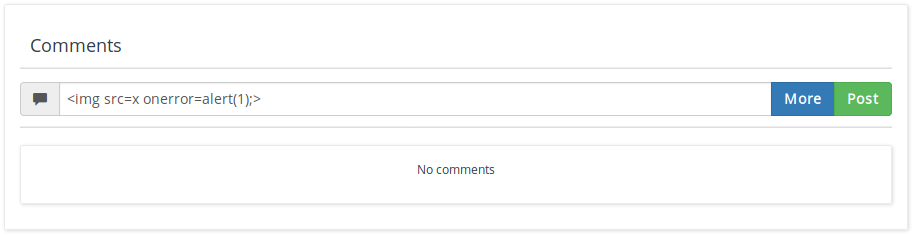
Proof of Stored XSS: