AttackDefense.com [SXSS] - Concrete5 CMS
Mission
In this exercise, the attacker already has admin access, so there is nothing more to be done. However, it looks like that admin access does lead to an XSS attack. So you can try to find this XSS as a purely academic exercise.
A version of Concrete5 CMS is vulnerable to a stored cross site scripting attack. The following username and password may be used to explore the application and/or find a vulnerability which might require authenticated access:
- Username: admin
- Password: 123321
Objective: Your task is to find and exploit this vulnerability.
Level difficulty: Easy
Category: Real World Webapps > Stored XSS
Solution
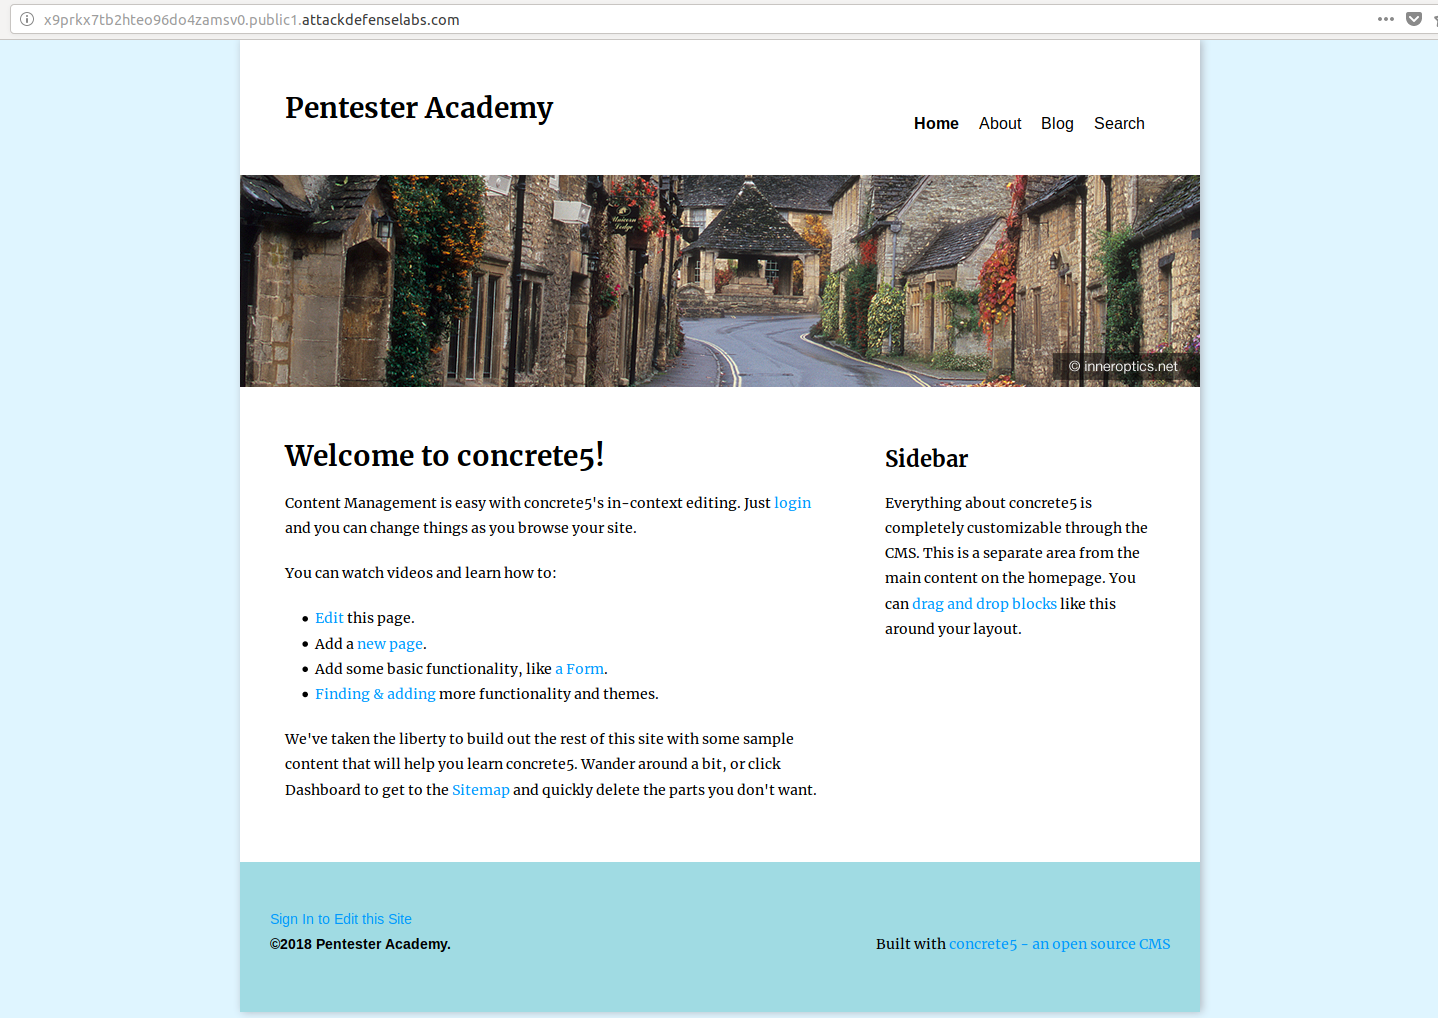
This time, I was provided with a full Concrete5 CMS website with multiple pages.
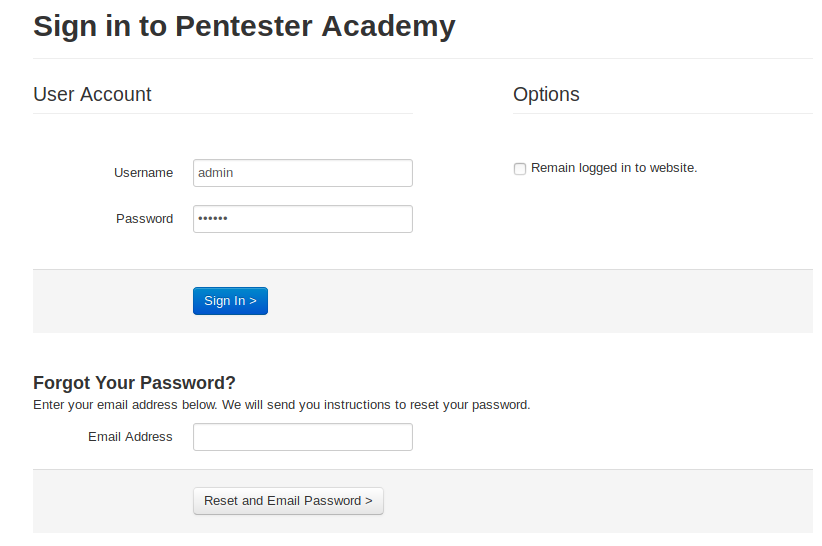
On the following page, I found the admin panel login, and I got access using the provided username and password.
By navigating the application control panel, I managed to obtain access to the environment variables at the following link.
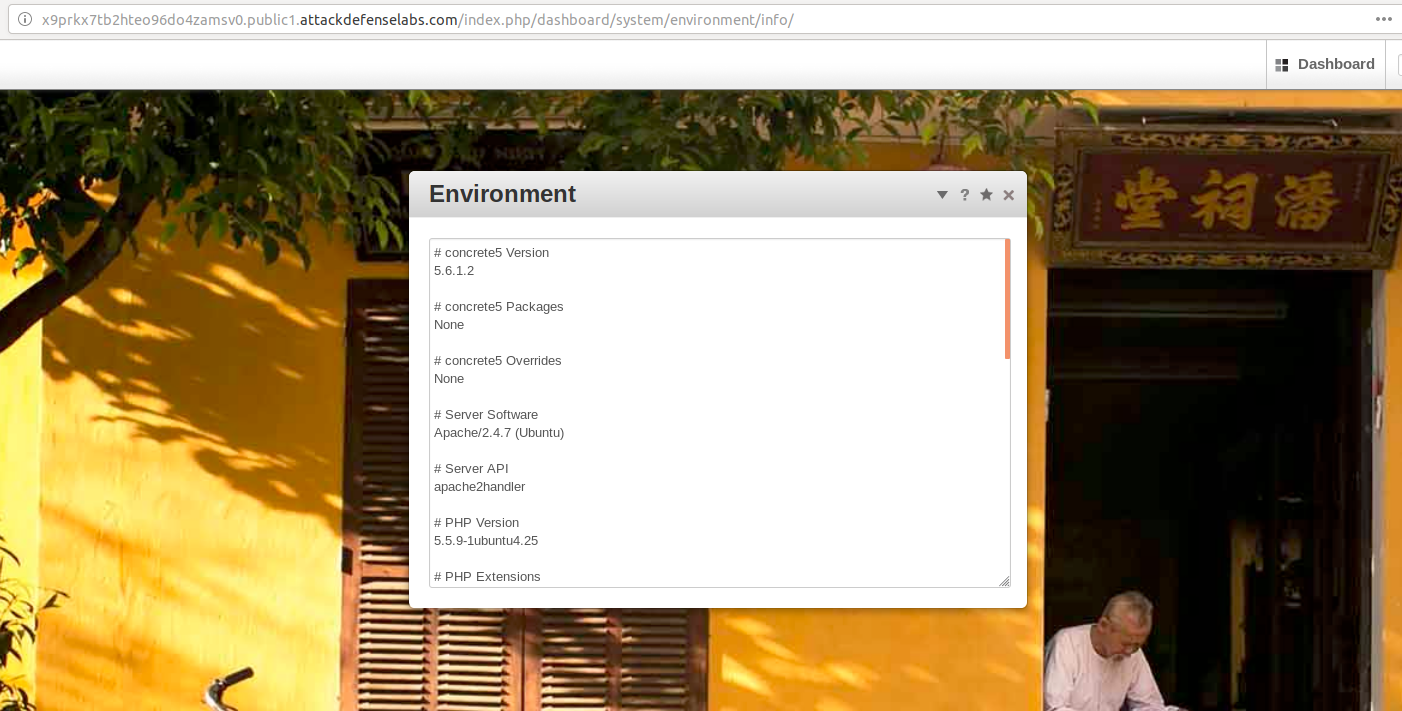
As we can see, the Concrete5 version is 5.6.1.2.
Again, I will use @GetSploitBot for Telegram in order to obtain exploits for my version of Concrete5.
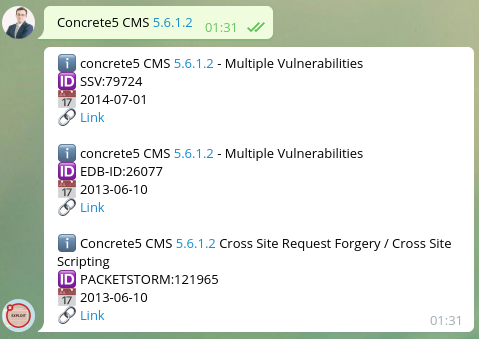
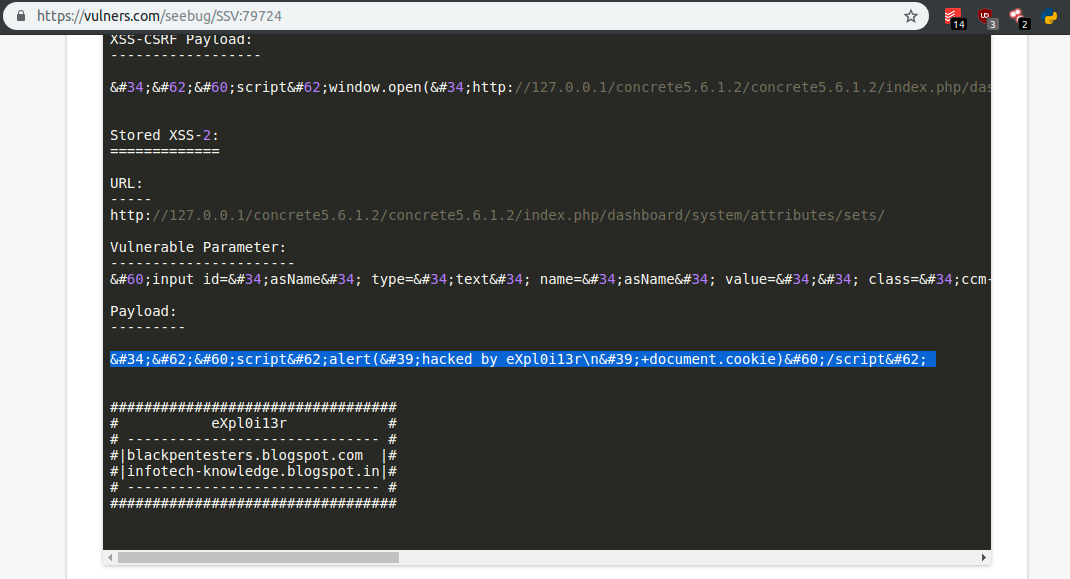
Following the above exploit, I was able to find the following path:
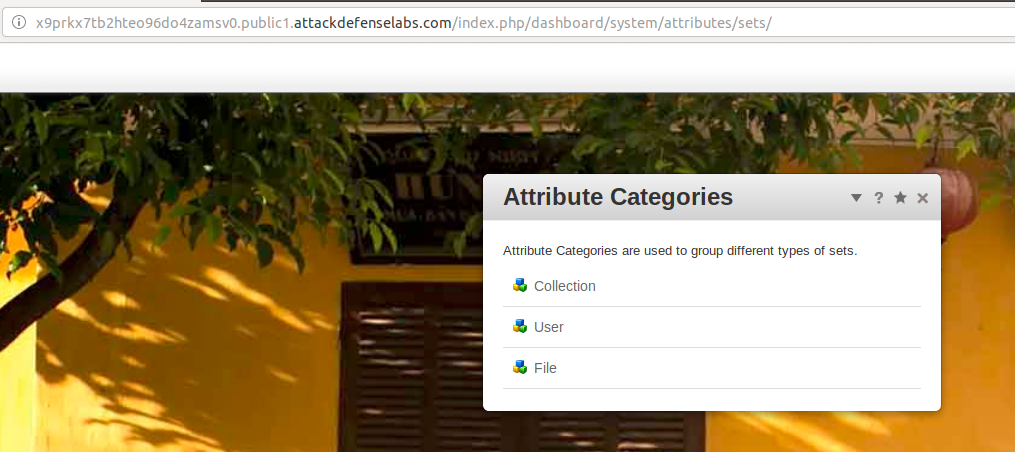
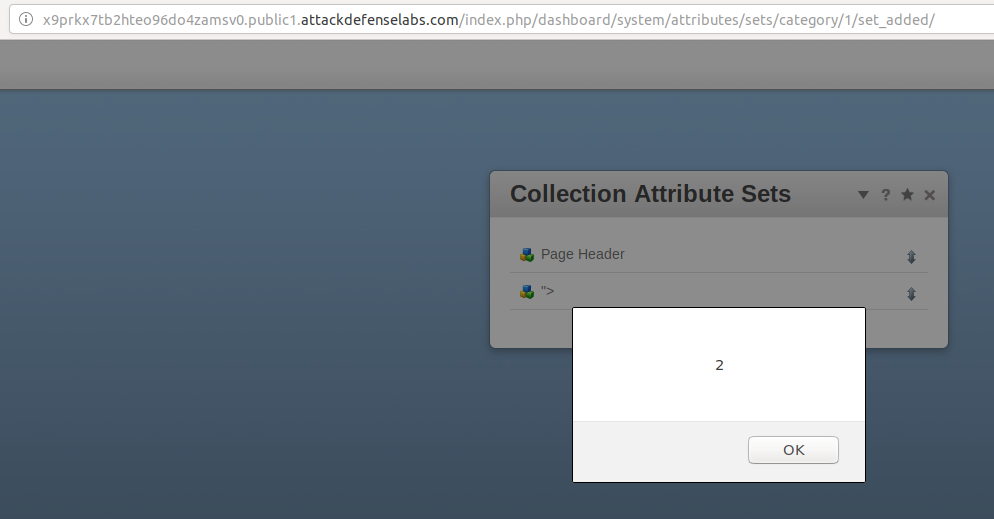
I decided to set my XSS payloads at http://x9prkx7tb2hteo96do4zamsv0.public1.attackdefenselabs.com/index.php/dashboard/system/attributes/sets/category/1/, as seen in the example below:
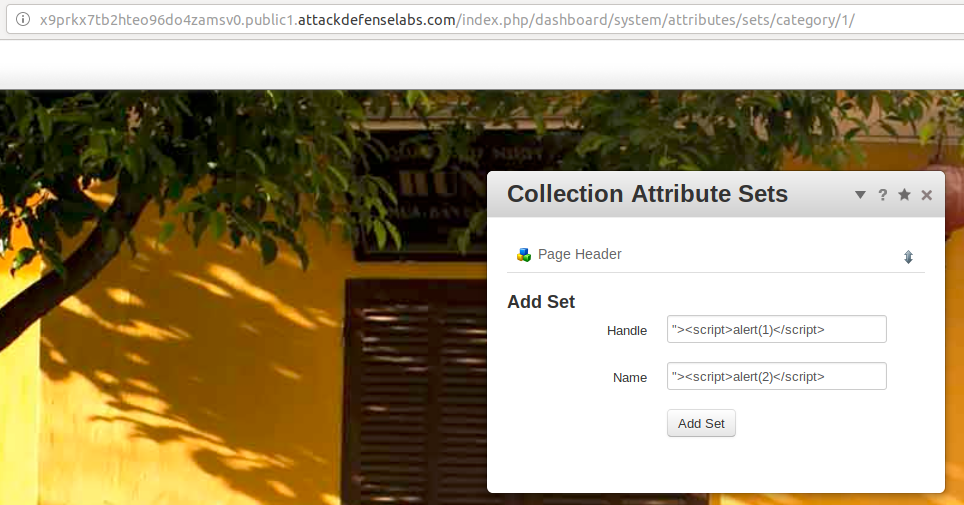
Result of my payloads: