AttackDefense.com [SXSS] - ApPHP MicroBlog
Mission
A version of ApPHP MicroBlog is vulnerable to a stored cross site scripting attack. Your task is to find and exploit this vulnerability. Authenticated access is not required to exploit it.
Level difficulty: Easy
Category: Real World Webapps > Stored XSS
Solution
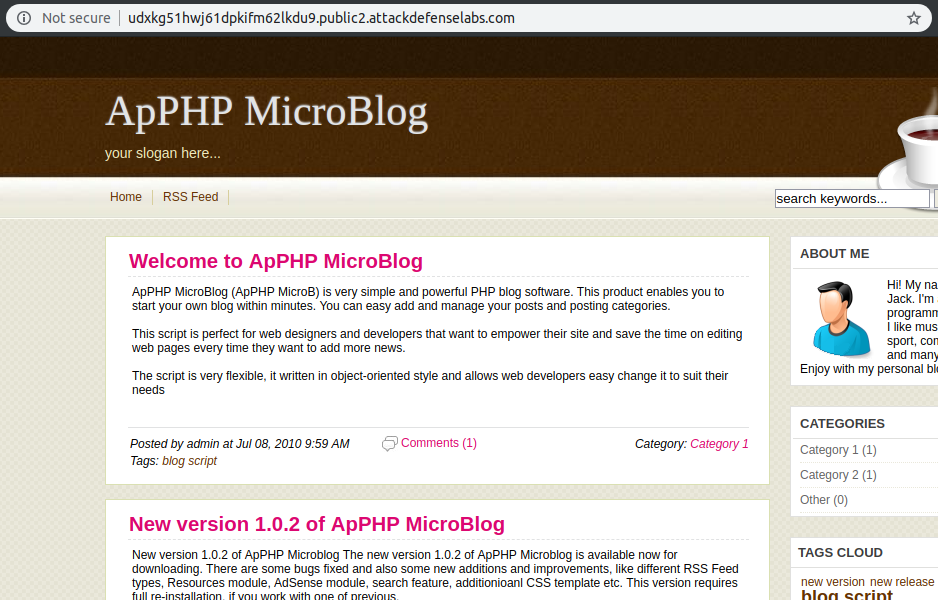
On this challenge, I was again provided with the same version of ApPHP MicroBlog as in the RCE exercise found here.
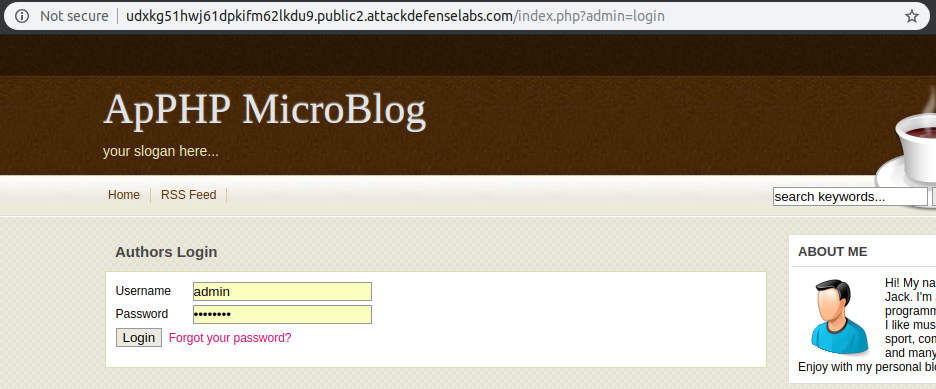
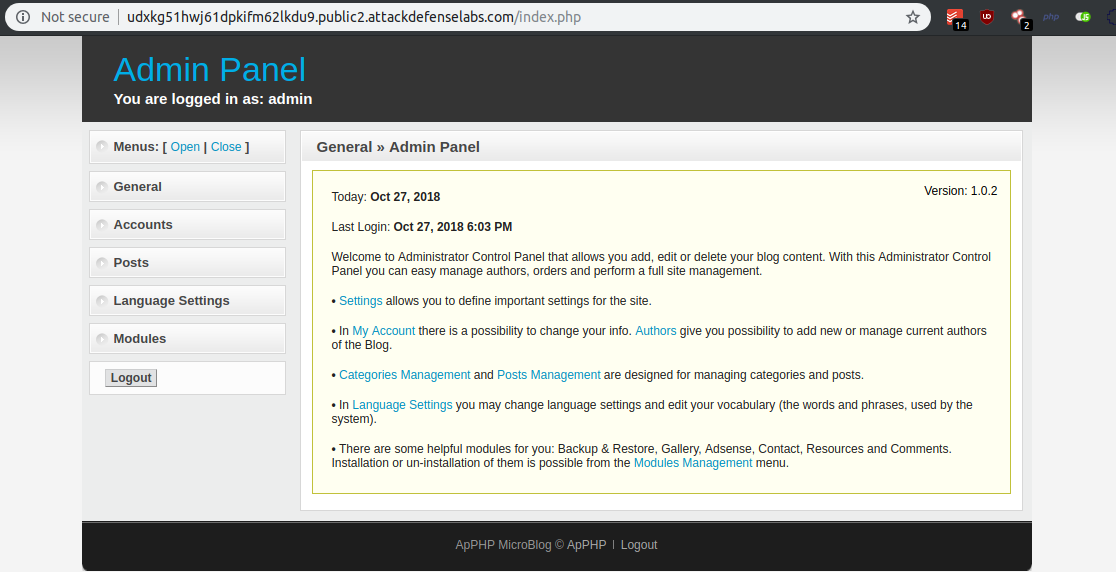
Therefore, I tried the same username and password (admin && password) as in the RCE challenge on the admin login form.
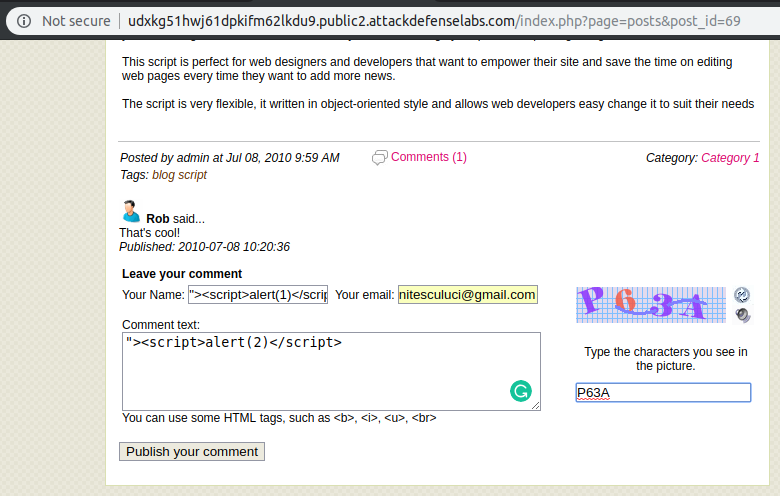
By going to an already posted article, we can observe the presence of a comment module within our blog. In that comment module, I used the following examples of XSS payloads.
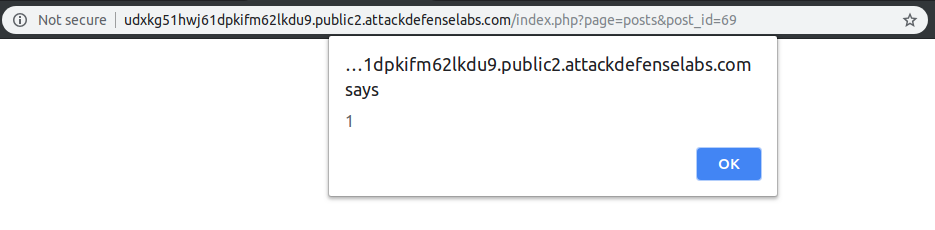
With a simple refresh, I obtained the following result:
This post is licensed under CC BY 4.0 by the author.