[OtterCTF 2018] - Otter Leak Writeup

Description:
We found out that one of the Otters has been leaking information from our network! Find the leaked data.
Format: CTF{flag all uppercase}
Solution Author:
Lucian Nitescu, as part of jmp 0xc0ffee team.
Stats:
200 points / 45 solvers
Solution:
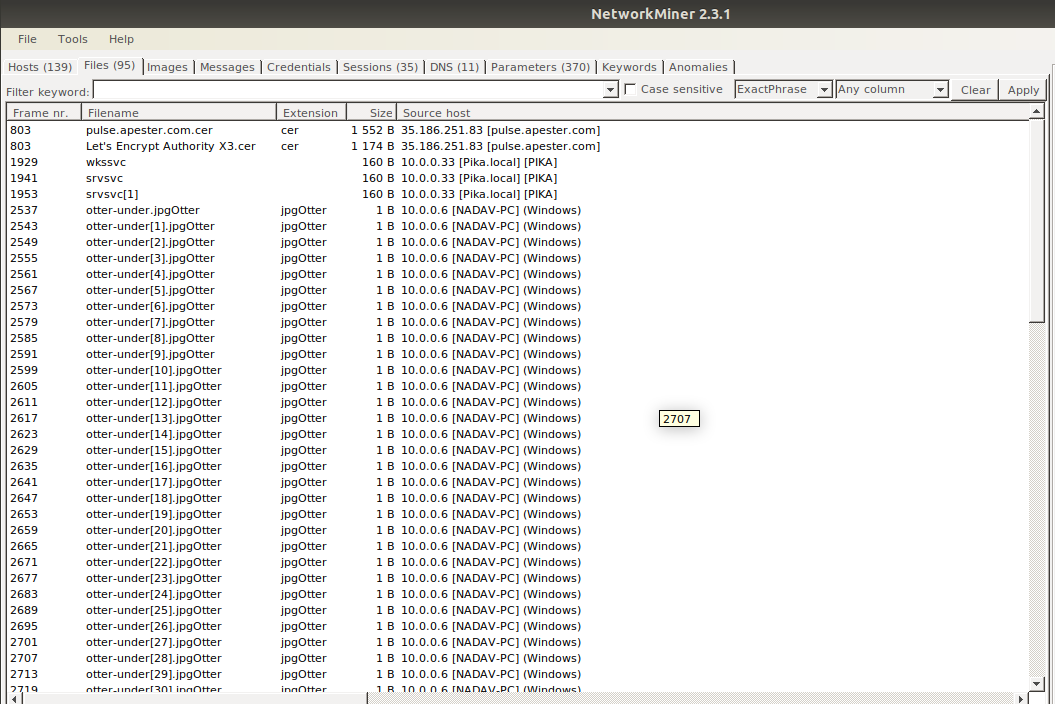
On this challenge, I was provided with a .pcap file which contained packets from an internal network. My first step with every pcap file is to launch the Network Miner tool and take a look at what it retrieves. Here I discovered the following files:
Because Network Miner is a good tool, but not a perfect one, I had to launch Wireshark and extract all the files sent by the 10.0.0.6 host over the SMB protocol.
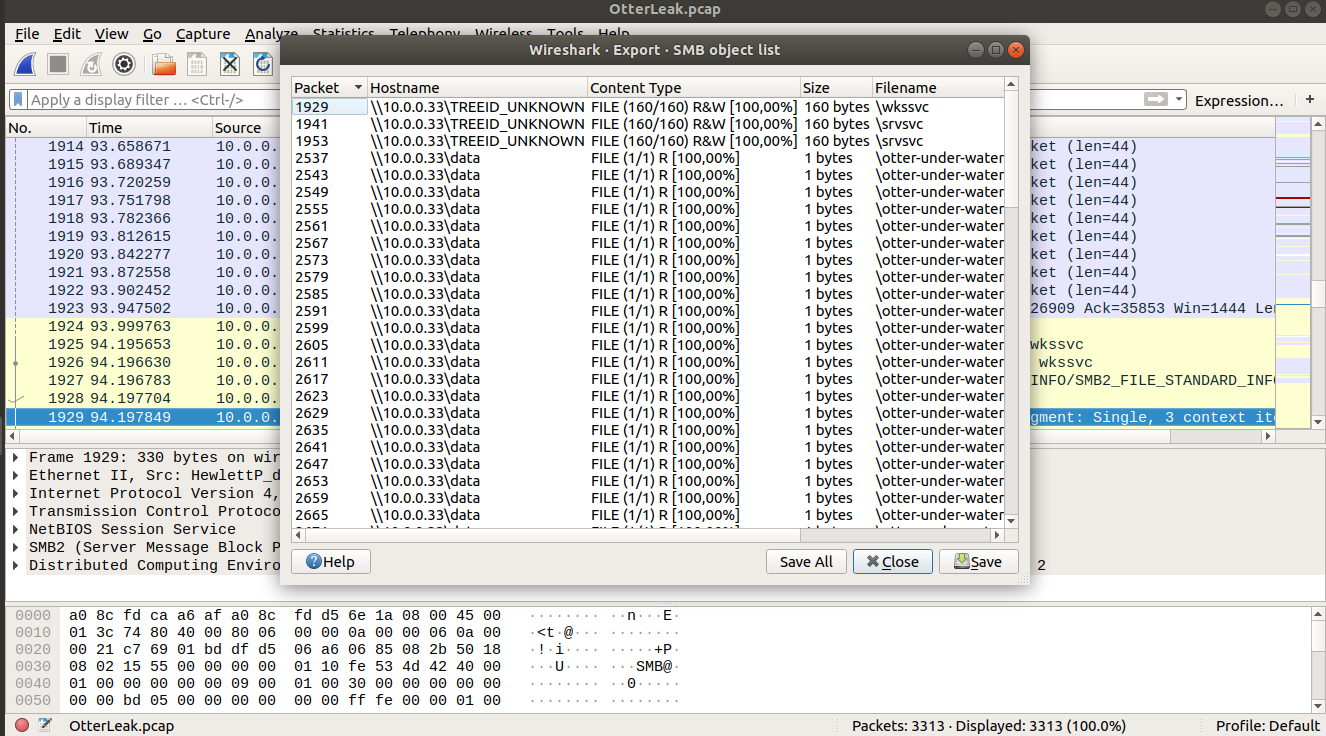
Output of the Wireshark file retrieval:
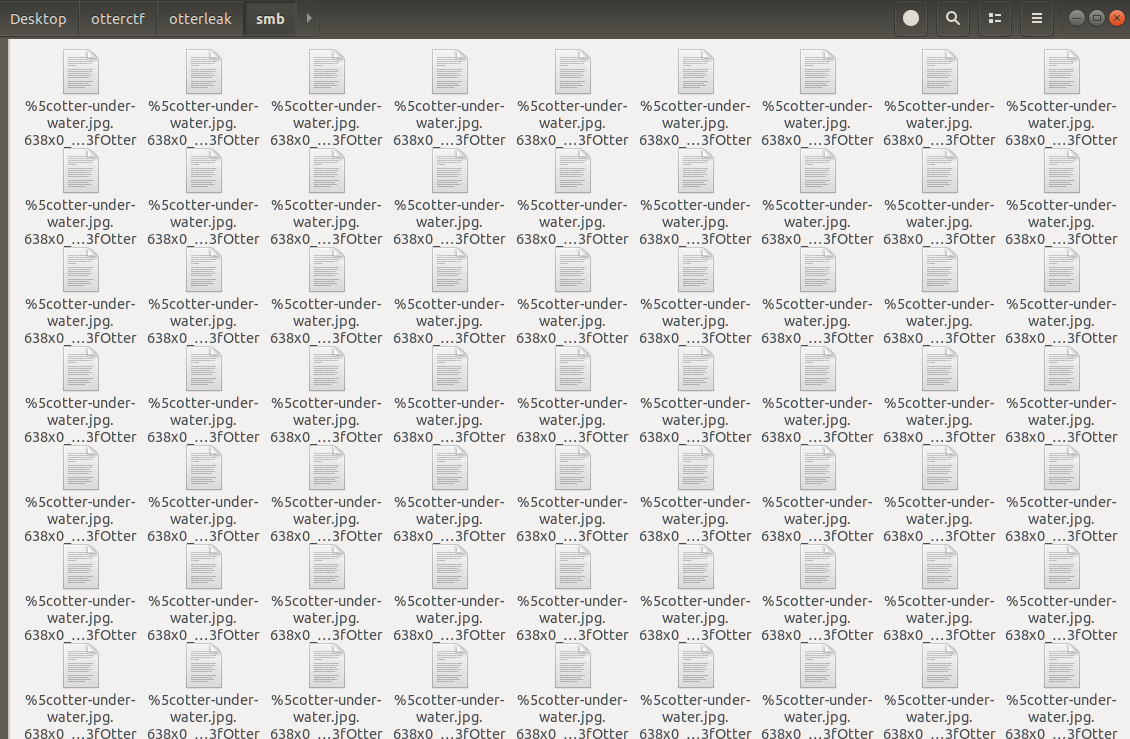
At this point, I discovered that all the files have the .jpg extension but contain only one character each. Let’s read them all at once!
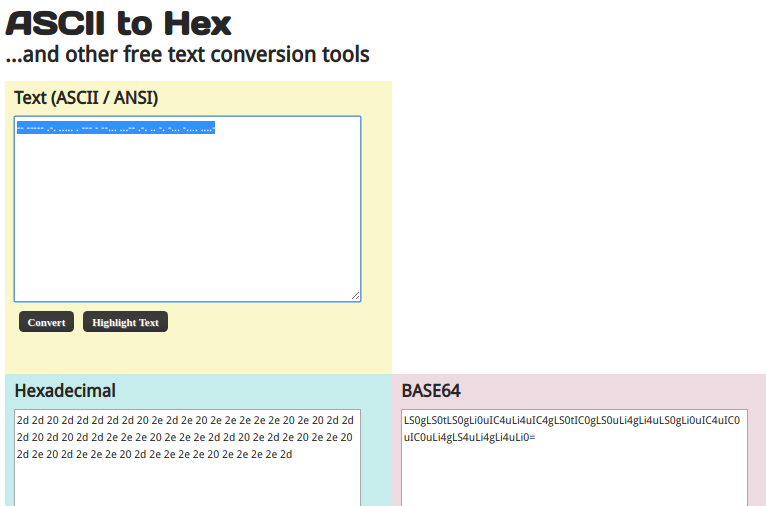
As you can see in the following image, on the first row I got a string that looks like base64 encoding:

I decided to decode my string, and I obtained the following Morse code:
I decoded the Morse code and obtained the flag:
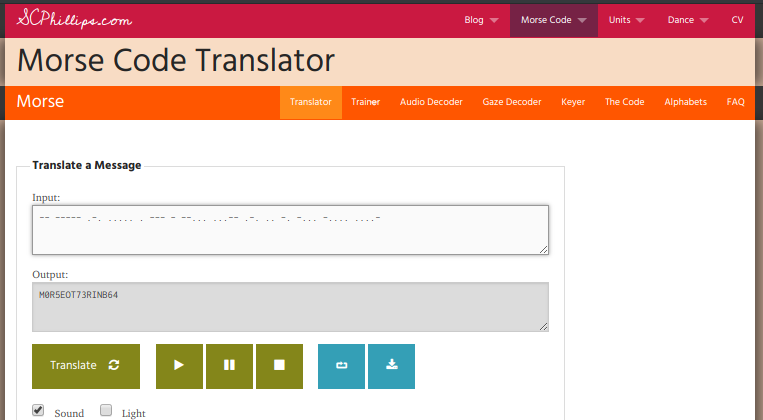
I added the missing parts of the flag in order to respect the required format.